Atlas Sylo
Let agents use real systems. Never hand them the keys.
An agent that needs GitHub, Slack or an internal API usually gets a copy of the key. Sylo keeps the key in the gateway, checks each request against your rules, and records every action.
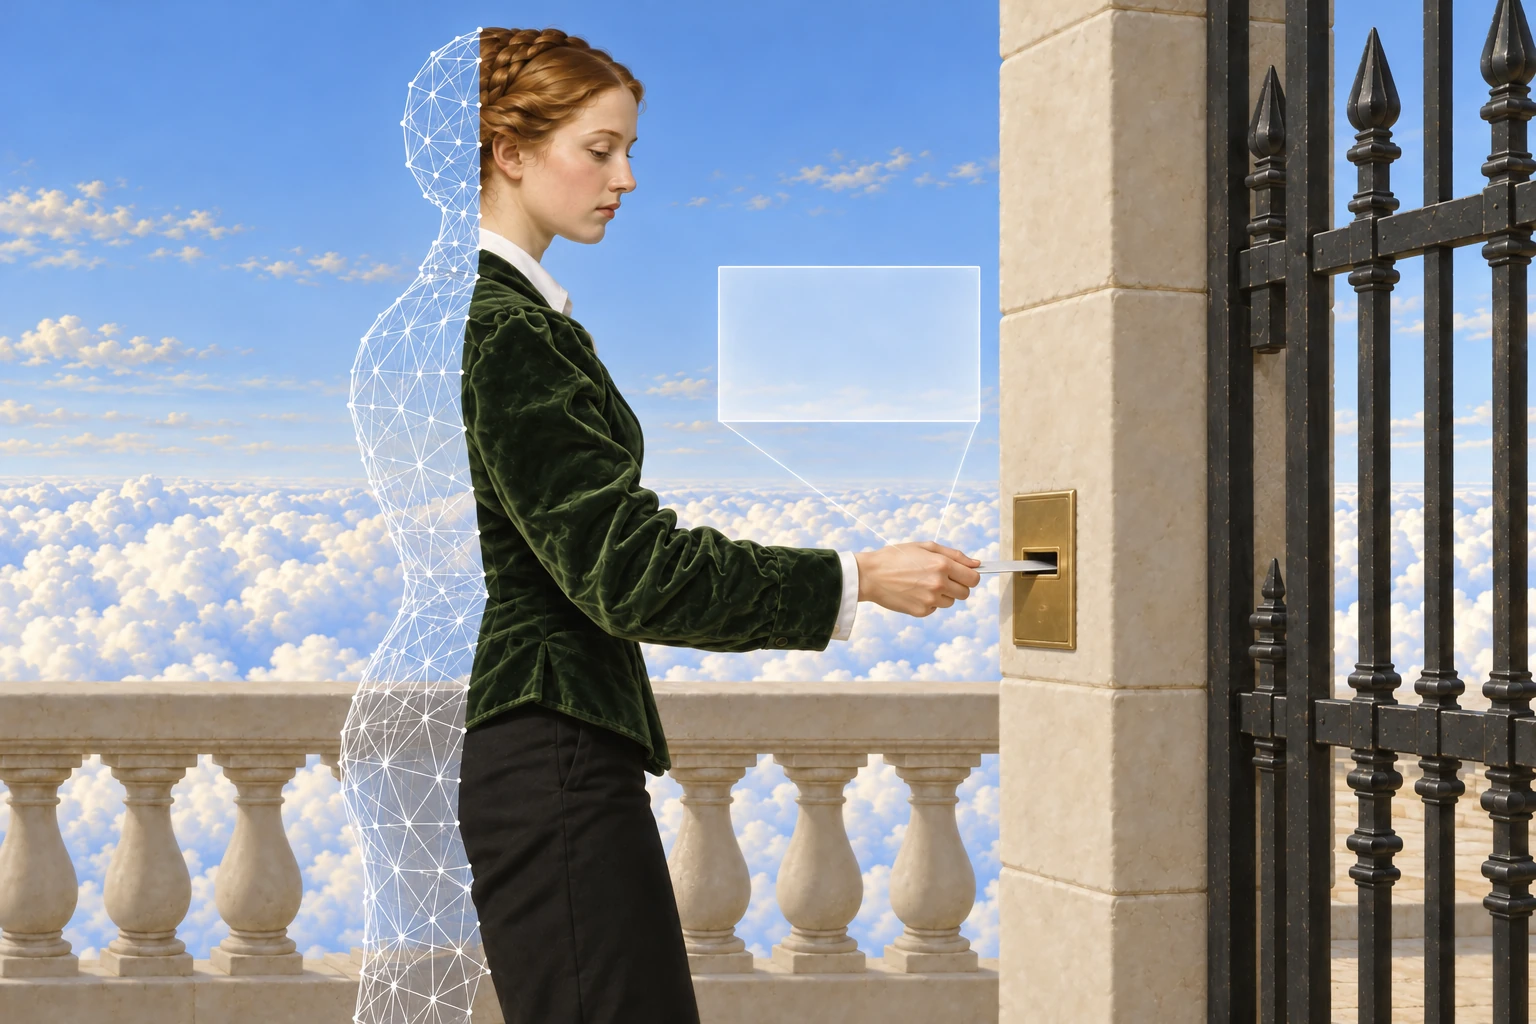
Control at the boundary
session token, no credentials Sylo policy
- destinations and services
- access rules
independent recordmaintained outside the agent
- Agent requestoutbound request
- Sylo policydestinations and servicesaccess rules
- Credentials are injected at the gateway.
- Approved service
- Record written
What Sylo does
Put control where actions happen.
Connect
Route the agent’s web and MCP traffic through Sylo. Works with E2B, Docker, Modal and any container.
Isolate
The real key stays in the gateway. The agent holds a session token with no credentials in it.
Identify
Every request resolves to an agent, a run, an owner and the person who started it.
Control
Rules allow, watch or deny by service, destination, method or MCP tool. The stricter rule wins.
Explain
A denied call returns the rule that matched, a request ID and the next step.
Stop
Security can revoke a run and read the ordered record of request, decision and result.
Why Sylo
Control that sits outside the agent.
Works with agents you built elsewhere. Runs under every Atlas deployment. Controls only the traffic that passes through it.
What you can measure
Five numbers for the next security review.
Rows 1, 2 and 4 are true by design. Rows 3 and 5 are what you report back after a pilot.
1
Standing credentials reachable by agents
Count keys, tokens and service accounts in agent environments
Zero on governed agents
2
Agent actions with full attribution
Agent, run, owner, initiating person on each call
100% on governed path
3
Out-of-policy calls blocked
Count per month, by agent and destination
Tracked; the breach proxy
4
Time to revoke a misbehaving agent
Seconds from decision to cut-off, one console
Under a minute
5
Security review time per new agent
Hours: first agent vs next agent on an approved profile
Down, measured per pilot
How it comes together
From first call to production.
One protected request
Install the SDK, create a session with credentials and rules, start the agent.
Watch, then enforce
Run rules in watch-only mode on real traffic, then switch to enforce.
Save it as a profile
Security reviews the rules once, then applies them to every run.
Explore where it fits
Bring one agent.
Tell us what it needs to call and what it must never do.